
Practical security
Scanner alert or confirmed vulnerability? How to tell
By Qlinnt · Updated
A scanner alert is an observation that needs context. Confirm what was measured, reproduce the condition with permission, then assess impact separately. A missing header, redirect or suspicious string does not by itself prove exploitation.
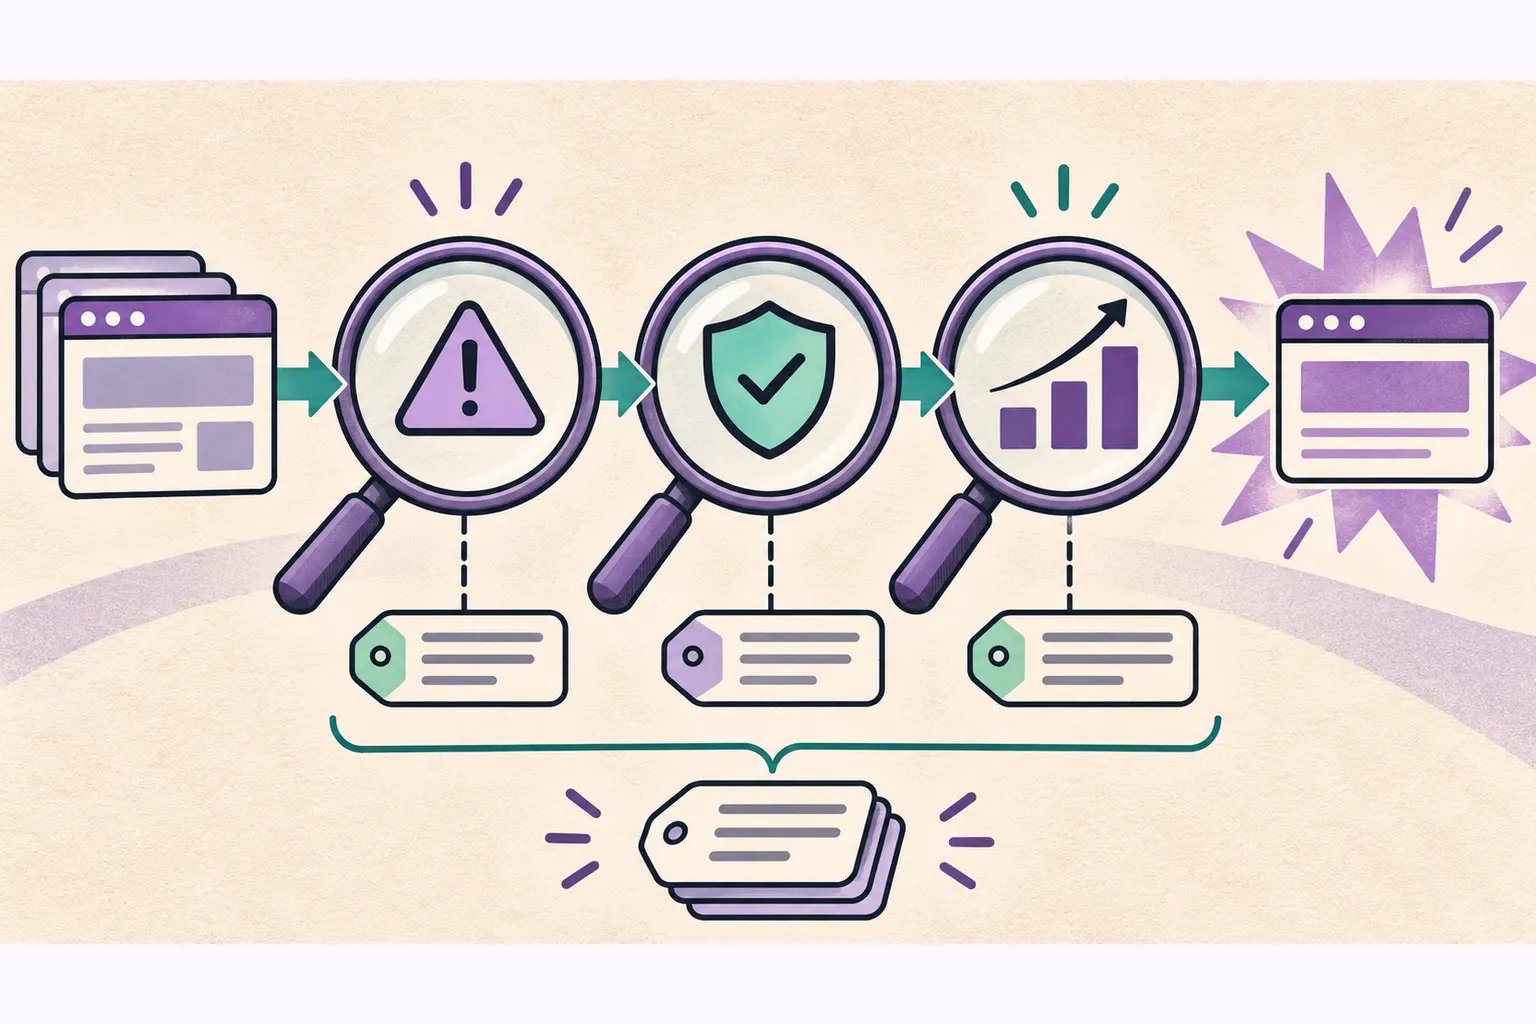
Understand the problem before changing your site
A report can be technically accurate and still be easy to misread. A response may lack a defensive header, yet there may be no injection path. A redirect may be intentional. A table may allow anonymous reads because it is a public catalog. The finding becomes useful when the report explains the observed condition and the unanswered question.
Use three separate levels: signal, validated condition and demonstrated impact. Severity describes priority, not certainty. An alarming title does not strengthen evidence, and a confident explanation from an AI model does not replace a reproducible test. Start by asking what a second reviewer could actually verify.
What to review and how to reduce risk
- Record the affected route, the check and the exact observable condition. Redact credentials and personal information.
- Repeat the observation in staging with synthetic data. Keep the request, browser version and relevant configuration.
- Identify prerequisites: authentication, HTML injection, another proxy or access to a specific record. Mark unknown prerequisites as unknown.
- Ask an authorized specialist to validate exploit chains that need unusual requests, server desynchronization or changes to application state.
- Prioritize by reachable data and business impact, then fix the shared cause and repeat the original test.
How to verify it with safe tests
For a safe exercise, remove a security header from a local fixture. Confirm that the scanner reports the missing header. Restore it and rerun the same route. This validates a configuration check; it does not prove that the first fixture was exploitable.
Keep a negative control with the header present. A useful detector should preserve that case, identify the changed fixture and state its coverage. If the target could not be loaded, record an inconclusive result instead of a pass.
What Qlinnt can check and where its scope stops
Qlinnt reads the public surface and reports bounded evidence. It does not perform request-smuggling exploitation or establish that credentials were stolen. HTTP header injection and server desynchronization require tests beyond a DOM inspection.
After a correction, a clean result only addresses the condition that was actually checked. Review the same header template, component or policy on other routes. Use the related fix-verification guide to avoid mistaking a failed or incomplete scan for a resolved issue.
Does a critical label prove exploitation?
No. Severity and confidence are separate. Ask for prerequisites, evidence and the test that established impact.
Can I validate findings on another company's site?
Only within explicit authorization and scope. Use local fixtures or your own staging environment for these exercises.
Sources and further reading
Review your website's public surface
Scan a website you own or are authorized to assess. Verify your email to read the free diagnosis. The scan does not replace code tests or a specialist assessment.
Scan my website for free