
Practical security
CSP form-action and Report-Only: what your policy really blocks
By Qlinnt · Updated
An enforced CSP and a Report-Only policy do different jobs. Multiple enforced policies intersect. Script directives have fallback rules, but form-action does not inherit default-src. Review those controls separately and fix HTML injection at its source.
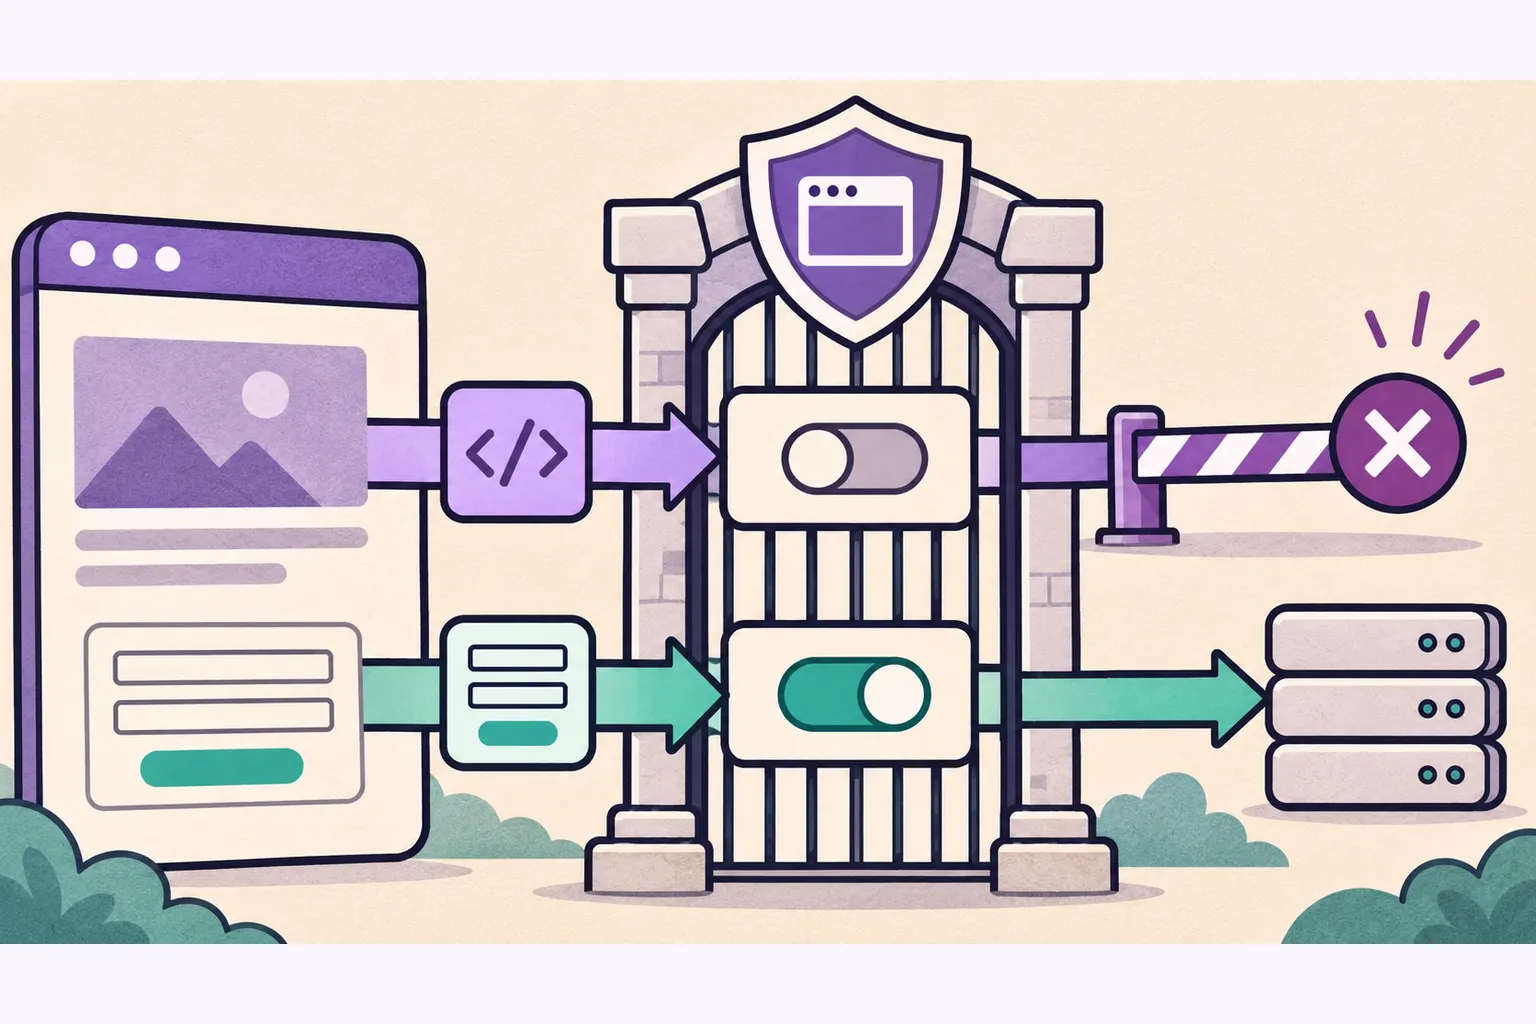
Understand the problem before changing your site
A header named Content-Security-Policy is not a complete description of what a browser allows. A reporting policy can observe violations without blocking them. An additional policy can further restrict a permissive one; combining their allowlists into a union gives the wrong answer.
For script elements, script-src-elem takes precedence over script-src, which falls back to default-src. Inline scripts also depend on nonces and hashes. Form submissions have a separate form-action directive with no default-src fallback. A script-blocking policy therefore says nothing by itself about every form destination.
What to review and how to reduce risk
- Inspect the headers of the actual final document, including repeated CSP headers and Report-Only headers.
- Evaluate every enforced policy independently, then intersect their restrictions. Do not merge allowed destinations into a union.
- Resolve the directive that actually governs script elements. Review nonces and hashes before interpreting unsafe-inline.
- Set form-action to the destinations your forms need. A self-only destination can be appropriate and is not proof of a credential leak.
- Fix unsafe HTML insertion, review Referrer-Policy and test legitimate forms before deploying a changed policy.
How to verify it with safe tests
In staging, prepare paired pages: one with only Report-Only, one with enforcement; one allowing inline scripts and another policy blocking them; one with default-src none but no form-action. Use fake form values and harmless script markers.
Observe actual behavior in the browser and compare it with the scanner's reported condition. Keep response headers, the final URL and browser version. A blocked marker tests that condition, not every external script, redirect or future injection path.
What Qlinnt can check and where its scope stops
Qlinnt now distinguishes response-policy enforcement, combines multiple policies, resolves inline script-element fallback and checks for an explicit form-action. Findings are configuration review opportunities, not claims of XSS or stolen credentials.
The check does not fully evaluate meta policies, external-script trust, every source expression or a multi-step data-exfiltration chain. Response-header nonces are not retained in its evidence. Do not treat a passed subcheck as a complete CSP audit.
Does default-src none block form submissions?
It does not provide the form-action fallback. Define form-action separately for the intended destinations.
Is form-action self unsafe?
Not by itself. Risk depends on injection, application behavior and the destination. Its presence is not proof of theft.
Sources and further reading
Review your website's public surface
Scan a website you own or are authorized to assess. Verify your email to read the free diagnosis. The scan does not replace code tests or a specialist assessment.
Scan my website for free